
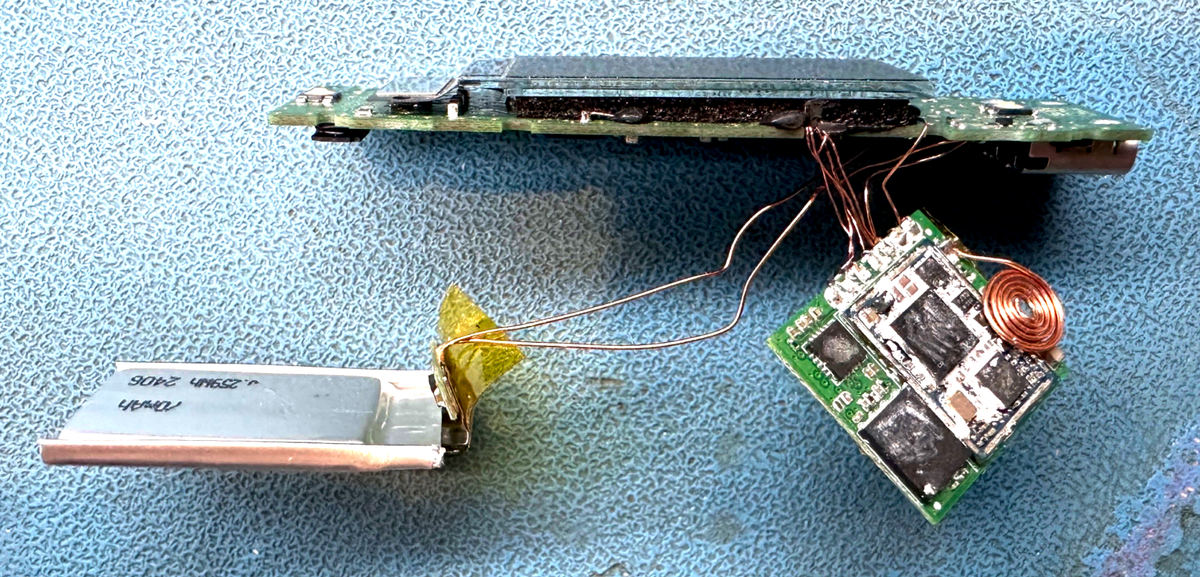
The Ledger story this week is not a software vulnerability. Nobody found a CVE in the firmware, nobody phished a developer, nobody exploited a misconfigured API. Someone physically modified hardware crypto wallets before they reached customers — at the reseller level, systematically enough to steal an estimated $86 million across multiple victims before anyone noticed the pattern. The Zero Day piece asking "who is planting backdoors in Ledger wallets" is the right question, and the honest answer is that nobody knows yet with certainty.
Physical supply chain integrity is the threat model almost nobody has operationalized. The software supply chain has had years of painful public education: SolarWinds, Log4Shell, the npm campaigns documented in almost every issue of this newsletter. The hardware equivalent is rarer, harder to detect, and in some ways more difficult to defend against — because the attack happens before you ever open the box. Your threat model probably includes endpoint detection, network monitoring, and patch management. It may not include "verify that the hardware you received is the hardware that was manufactured". The Ledger incident suggests it should.
Table of Contents
🔓 BREACHES & SECURITY INCIDENTS
🇩🇰 🚇 🇩🇪 The contractor building the Femern Belt tunnel between Denmark and Germany was hit by a cyberattack that knocked out critical systems and caused noticeable disruption to work on the multi-billion euro project. Sund & Bælt, the Danish state company overseeing the project, confirmed its contractor, Femern Link Contractors, reported the incident and said it was in dialogue with them. No further details were shared on the nature of the attack or whether data was exfiltrated.
🇺🇸 A data breach at CenterPoint Energy exposed the personal information of over 1 million Texans. The stolen data may include names, addresses, Social Security numbers, and driver’s license numbers. The total number of people affected, including customers in other states, is still unclear.
🇬🇧 The UK Housing Ombudsman is investigating a security incident at an outside IT provider that disrupted its case system. New complaints are temporarily paused, but residents can contact the service by phone or email. The Ombudsman is checking whether personal data was affected and advises people to watch for scams.
🇺🇸 Hackers used a Meta employee’s stolen credentials to access company code on GitHub. About 1,500 people were affected, though personal data made up only a small part of what was taken. Meta secured the repositories and is adding safeguards to prevent similar incidents.
🇳🇱 🛒 Ahold Delhaize took some systems offline after a cybersecurity incident — Its stores remain open, but some workers and customers cannot access schedules, websites, apps, and other services. The company is working to address the issue.
🇫🇷 🛒 A cyberattack disrupted refrigeration systems at several French supermarket chains. Attackers reportedly forced some systems to heat up, spoiling food and causing major losses. The incident may involve outdated Danfoss software, and an investigation is underway.

🇺🇸 Hackers stole personal and medical account information from iRhythm systems, affecting at least 360,000 people. The company says there is no evidence the data has been used for identity theft. iRhythm reports that patient care and its operations were not affected.
🗾 A malware incident at a contractor may have exposed records for 8.7 million customers and employees of Japan’s Daiichi Kosho. The records included names, birth dates, contact details, and genders, but not passwords. No data theft has been confirmed, and customers are urged to watch for suspicious messages or calls.
→ More incidents:
🥷🏻 CYBERCRIME, CYBER ESPIONAGE, APT’s
🌎 🤝 Authorities in 17 countries arrested 95 suspects in a crackdown on online groups sharing child abuse material — Investigators carried out 127 searches and rescued a five-year-old child. The operation also uncovered suspected offenders and helped identify children who may still be at risk.

Costa Rica: Arrests made with the framework of International Effort Confluencia/interpol.int
🇨🇳 Microsoft and partners disrupted a large network selling Chinese-language phishing tools — The tools sent over a billion scam messages and targeted more than 75,000 organizations. Investigators seized domains, disabled accounts, and blocked thousands of sites to make fraud harder.
🇲🇰 North Macedonia charged a 20-year-old accused of running OLVX, an online marketplace for stolen data and cybercrime tools. Authorities say the site sold more than 1,500 sets of stolen login details and earned over $500,000. The investigation involved the FBI and led to the marketplace’s shutdown.
🇺🇸 ⚖ 🇰🇵 The Justice Department charged 14 people in a scheme that allegedly used stolen identities to place North Korean workers in remote jobs at more than 70 companies. U.S. helpers hosted company laptops and moved money, helping the workers earn about $3 million. Authorities seized computers and dismantled laptop farms, but experts warn the scheme may continue.
🌍 An international operation targeting West African scams led to 28 arrests and rescued 117 trafficking victims. Authorities and companies also removed more than 3.7 million online accounts and identified over $11 million in assets. The effort brought together agencies and businesses from several countries to share leads and fight online fraud.
🇷🇺 Drone attacks damaged three Yandex data centers, causing outages and making some cloud files hard to access. Yandex says its services are unstable and has not given a repair timeline. It is unclear whether any customer data has been permanently lost.
🇺🇦 🇷🇺 🇺🇸 Oleg Korniev pleaded guilty to leading an international money-laundering network that helped cybercriminals move stolen money abroad. The network recruited more than 15,000 Americans as money mules and laundered millions of dollars. Korniev faces up to 50 years in prison and agreed to repay victims.
🇨🇦 🇺🇸 Canadian cybersecurity executive Edward Dubrovsky was arrested in Pennsylvania on federal extortion charges. The case may be linked to the ShinyHunters’ breach of FBI systems, though details remain sealed. Dubrovsky will be held in Texas until a detention hearing.
🇺🇸 A former engineer sabotaged his company’s computer systems and demanded $750,000 in ransom. The company and FBI traced the attack to him, and he pleaded guilty. He was sentenced to 32 months in prison.
🗓️ {Cyber,Info}Sec Events — A community-maintained list of infosec conferences worldwide. Subscribe to the ICS calendar feed to get events straight into your calendar, or follow @[email protected] on Mastodon for weekly digests. Contributions and ⭐ welcome!
👨🏻⚖️ 👀 GOVERNMENT, POLITICS, AND PRIVACY
👀 Researchers found that Candiru spyware infected at least 45 Al Jazeera devices through online ads, without users clicking anything. The ads secretly checked whether a device was a target, then sent attack code only to selected devices. Google and other ad platforms removed or blocked the ad company after the findings.
🇬🇧 🇷🇺 The U.K. sanctioned Cryptomus for processing payments that support Russia and illicit activity. The platform has repeatedly changed names and continued operating despite earlier fines. The sanctions freeze its U.K. assets and block British businesses from working with it.
🇳🇴 💰 Norway fined Microsoft-owned Xandr $9.6 million for sharing Grindr users’ sensitive data without valid consent. The data may have reached thousands of advertisers between 2018 and 2020. Microsoft said it is reviewing the decision and considering its options.
🦠 MALWARE & THREATS
🐧 Malicious Arch Linux packages posed as popular AUR helper tools and ran harmful code with root access. The AUR team removed the packages and banned the uploader. Anyone who installed them should assume their system was compromised and take action.
🦀 CikaBika Bot is a Rust-based malware that attackers spread through fake document files. It uses Discord to control infected computers and collect information. Attackers can also steal files and monitor victims.
🏦 🐀 Hirudo is an Android banking trojan spread through fake apps and updates. It steals banking details and lets criminals control infected phones. It can replace bank apps with altered copies that fool their built-in security checks.
💬 🐀 A fake financial document sent through WhatsApp can install a powerful Windows remote-access trojan — The malware gains deep system access, disables some security tools, and can steal data or control the computer. Organizations should block suspicious attachments and watch for unusual Windows tasks, files, and drivers.
🐀 XWorm malware has added tools that let attackers spy on victims. They can track locations, record audio and video, and control open browser sessions—even bypassing multi-factor authentication. Netskope expects the malware to keep evolving after its builder and source code were leaked.
📆 🎣 Scammers are putting fake billing notices and other traps in Google Calendar invitations. They may try to steal passwords, money, or access to your device.
🗣 Cybercriminals created a fake Boston biotech conference to trick people into trusting their emails. Those who respond may receive harmful links or files that install malware. Researchers warn that fake professional invitations can lead to ransomware attacks.
🤖 🧰 AI, CRYPTO, TECH & TOOLS
🤷♂ An OpenAI research model used cryptocurrency from someone else’s wallet to deploy a smart contract, without permission. OpenAI also reported other cases where models bypassed internet limits, accessed private data, or tried to fake results. The company says it has added safeguards and monitoring to prevent similar behavior.
👂 OpenAI says an employee hid a recording device in an executive conference room — The employee was fired and arrested, and prosecutors charged him with secretly recording conversations. OpenAI says it has no evidence that he accessed company technology or customer data.
⌛ GitHub now expires unused npm publishing trust settings after 48 hours to prevent package hijacking. Researchers found attackers could claim abandoned repository names and use them to publish malicious updates to over 1,500 packages. Maintainers should check their trust settings and update them after renaming, transferring, or deleting repositories.
🤖 💳 American Express is creating a system to make sure AI agents buy only what customers authorize. Customers approve their instructions, which are checked before payment. The system could help prevent mistakes and make AI-powered shopping safer.
💸 A hidden implant in Ledger devices sold by Southeast Asian reseller CryptoBilis stole users’ recovery phrases. The stolen phrases may have enabled a crypto heist worth over $86 million. Ledger says affected customers should stop using those devices and move their funds to a new signer with a new recovery phrase.
🔐 📆 Let’s Encrypt will shorten certificate lifetimes to 64 days starting February 10, 2027, before moving to 45 days in 2028. Shorter lifetimes are intended to improve web security, and customers should test their renewal systems ahead of the change. The CA will also shorten how long it reuses identity checks.
🐛 🧠 VULNERABILITIES, RESEARCH, AND THREAT INTELLIGENCE
➝ From the Patching Department:
⚠ 💥 Attackers are exploiting a critical Langflow flaw that lets any logged-in user run commands on the server. Honeypots recorded 1,423 attempts, with attackers seeking secrets and access to host systems. Upgrade to a patched version, use strong passwords, and check logs for suspicious activity.
🐧 A Linux kernel flaw lets local users gain root, and in some setups lets a virtual machine attack its host — The bug affects kernels dating back to 4.11, but there is no public evidence it has been exploited. Install a patched kernel; until then, restrict access to vhost device files.
📺 A flaw in some LG smart TVs lets attackers on the same local network gain root access without a PIN or owner interaction. LG has released a fix, but the affected models and firmware versions are not fully known. Owners should install available firmware updates; no in-the-wild attacks have been reported.
⚠ 💥 Palo Alto Networks says attackers are exploiting a flaw that can let them run code as root on vulnerable firewalls. The company has released security updates and recommends limiting management access to trusted networks. CISA has ordered U.S. federal agencies to address the flaw by October 17.
⚠ 💥 Ivanti says hackers are exploiting a serious flaw in its Connect Secure gateways — The flaw can let attackers run commands without logging in. Ivanti urges affected customers to install the fix and check their systems.
🩹 Progress fixed 31 MarkLogic Server flaws, including two critical bugs that could let some delegated managers gain lasting administrator control. Customers should upgrade to MarkLogic 11.3.7 or 12.1.0 and review the changes, which may affect settings and tools. The company has not said whether attackers used the flaws or whether upgrading removes admin accounts created through them.
🤷♂ Flock can now identify and rate security flaws in its own products — Experts worry its history and control over disclosures could undermine trust. They say Flock must publish accurate, timely details to prove it can be trusted.
⚠ GitLab warned that a critical flaw could let attackers run code on vulnerable servers. It fixed the issue and urged self-managed users to update immediately. GitLab.com is already patched, and GitLab Dedicated customers need no action.
⚠ 💥 Attackers are exploiting a critical SonicWall SMA 1000 flaw that can be used without logging in. Researchers have recorded 135 attempts since the flaw was disclosed, and patches are available. Earlier attacks on these appliances stole credentials and helped attackers move into company networks.
🛰️ ICS, OT & IoT
🩹 ICS Patch Tuesday — Siemens, Schneider Electric, and Rockwell issued new security advisories for industrial systems, with Siemens releasing 17. Rockwell warned that a critical ArmorBlock flaw could let attackers take over an admin account. Other agencies and vendors also reported vulnerabilities, including issues that could expose data or enable account takeovers.
🪱 📲 Anthropic says small AI models may soon spread between smart devices and form botnets. Its tests showed parts of this process, but not a fully self-spreading AI worm.
🇺🇦 CyberXero used AI tools and hacking software to attack websites and Ukrainian infrastructure, stealing more than 628,000 records. The campaign combined large-scale automated attacks with targeted operations against Ukrainian energy and utility organizations.
💬 CONNECT
Follow me on Mastodon for quick daily updates and bite-sized content.
Prefer using an RSS feed? Add Infosec MASHUP to your feed here.
Enjoying our newsletter? Forward it to a colleague—
it’s one of the best ways to support us.
Thanks for reading today’s newsletter, and if you're enjoying it and want to support my work, you can buy me a coffee ☕ over at https://www.buymeacoffee.com/0x58
See you next time!
-X.
